MSPs Move Into the CISO Seat as Cyber Risk Gets Harder to Scale
 Editor
Sophos research finds 46% of customers already rely on MSPs for CISO-level responsibilities, as compliance, reporting and AI-driven risk reshape managed security services
Managed service providers (MSPs) are moving beyond the traditional role of managing IT infrastructure and security technologies to become de facto cybersecurity leaders for their customers. The shift is highlighted in Sophos’ 2026 MSP Perspectives Report, which finds that 46% of customers rely on their MSP to act as their CISO, while 84% of MSPs expect demand for CISO services to increase over the next 12 months.
The findings point to a fundamental change in the MSP business model. As organisations contend with increasingly complex cyber risks, regulatory requirements and a shortage of specialist security leadership, MSPs are being asked not simply to operate security controls but to provide strategic guidance on risk, governance, compliance and security investments.
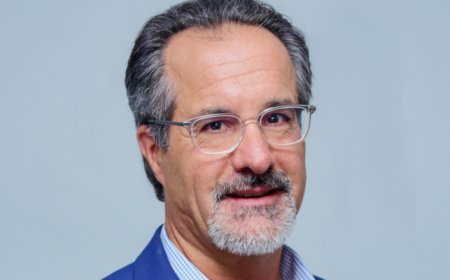
“Organizations require more than technology management to stay secure. They need trusted cybersecurity leaders who can help them understand their risk, navigate compliance requirements and translate security investments into meaningful business outcomes,” said Scott Barlow, Vice President and Chief Evangelist at Sophos.
For MSPs, the expanding CISO role represents both a growth opportunity and an operational challenge. Providing strategic security guidance across a growing customer base requires MSPs to standardise processes, improve reporting and reduce the amount of manual work involved in assessing and communicating cyber risk.
Fragmented tools challenge MSP scalability
The report highlights the operational burden behind the opportunity. MSPs estimate they could save 53% of their time if they had a single, unified platform for managing customer security posture, compliance and reporting. Meanwhile, 81% believe such consolidation could reduce the time spent on these activities by more than 30%.
The problem is reflected in current technology practices. While 36% of MSPs use a single tool or platform to centrally manage cybersecurity compliance or CISO-type activities, 53% rely on multiple tools or platforms.
“MSPs have an opportunity to become indispensable strategic partners to their customers, but scaling that role requires a more unified operating model.”
— Scott Barlow, Vice President and Chief Evangelist, Sophos
Security reporting presents a similar challenge. Although 86% of MSPs use fully or semi-automated processes to produce consolidated security posture reports, more than half—55% still require some manual effort. Only 31% can generate such reports quickly through a fully automated process.
For an MSP attempting to provide CISO-level services to dozens or hundreds of customers, these inefficiencies can become a significant constraint. The challenge is no longer simply acquiring cybersecurity expertise; it is creating an operating model that allows that expertise to be delivered consistently at scale.
Compliance becomes a strategic service
Compliance is emerging as another major driver of the MSP's expanding remit. According to the report, 99% of MSPs provide at least one cybersecurity compliance service, while 58% offer full compliance programme management.
Yet the breadth of services varies considerably. Only 6% of MSPs surveyed provide the full range of compliance services evaluated in the research.
Compliance also influences security purchasing decisions. On average, respondents said compliance affects 50% of their customers' cybersecurity purchasing decisions, with 33% describing regulatory requirements as heavily or decisively influential.
At the same time, only 33% of MSPs say they are completely confident in their ability to continuously monitor, manage and document compliance across multiple customers.
This gap between customer expectations and MSP operational capability could become increasingly important as organisations move from periodic compliance exercises towards continuous security and compliance monitoring.
Turning the CISO role into a managed service
Sophos is positioning its forthcoming Sophos CISO Advantage, scheduled to become available in October 2026, around this emerging requirement. The offering is designed to help MSPs structure the CISO responsibilities they already perform into a scalable and billable cyber programme management service.
Delivered through Sophos Fusion, the company's AI-native cybersecurity defence system, CISO Advantage uses AI-assisted assessment, reporting and roadmap workflows to provide board-ready insights, framework-mapped evidence and prioritised action plans across customer environments.
“Bringing security posture, compliance management and reporting together can help MSPs spend less time manually consolidating information and more time helping customers reduce risk, strengthen resilience and make informed cybersecurity decisions,” Barlow said.
The broader implication is that the MSP market is evolving from technology administration towards managed cyber-risk leadership. For customers without dedicated security executives, the MSP can increasingly become the bridge between security operations and business-level risk management.
For MSPs, however, capturing that opportunity will depend on whether they can make CISO-level guidance repeatable, measurable and scalable particularly as AI accelerates both the complexity of cyber threats and the expectations placed on security providers.
The MSP Perspectives 2026 Report is based on an independent survey of 800 MSPs across the US, UK, Germany, France, Singapore, Australia and Brazil. The research was conducted by Vanson Bourne in April 2026 on behalf of Sophos, with respondents ranging from senior to board-level MSP stakeholders.